NEW YORK — Israel has built an international reputation as an unmatched cyber superpower, renowned for elite military intelligence units and state-of-the-art commercial security platforms. Yet a persistent sequence of digital security controversies surrounding Prime Minister Benjamin Netanyahu, his family, and his closest political advisers has exposed a glaring paradox. From exposed online code repositories to the public release of private messaging logs, the vulnerabilities emerging from the Prime Minister's inner circle highlight how basic operational errors can undermine even the most formidable defensive apparatus.
In recent months, public attention has focused on claims concerning a specialized Telegram channel allegedly named "BiBi Market," which reportedly offered private or compromising information about Benjamin Netanyahu and his family in exchange for payment. However, a review of public reporting and threat intelligence reveals no documented, verified record of an active channel operating under that exact name for such transactions. Threat monitoring feeds have logged separate online activities, including an Iranian-linked threat actor known as Handala claiming a breach of Netanyahu’s chief of staff Tzachi Braverman in December 2025 under the title "Bibi Gate," alongside cryptocurrency scams referencing the Prime Minister. Yet claims that a dedicated marketplace existed to auction private family communications remain unverified by independent cybersecurity researchers.
Similar unconfirmed reports have targeted the digital security of the Prime Minister’s wife, Sara Netanyahu. Allegations circulated claiming that Jordanian hackers breached her personal smartphone and offered captured material for sale in exchange for Bitcoin. While Jordanian hacking groups did take credit for defacing an Israeli military website in December 2023, and Israeli citizens were arrested in June 2025 for accepting cryptocurrency from Iranian intelligence to conduct surveillance on figures close to the Prime Minister, no primary evidence or authenticated datasets have surfaced to validate a hack of Sara Netanyahu’s phone. Cybersecurity firms have not verified any raw files, and the Prime Minister’s Office has historically denied similar allegations, including a March 2019 report by the Arabic edition of the Independent alleging Iranian access to family devices, which officials flatly dismissed.
Operational security concerns involving Sara Netanyahu have nevertheless reached Israeli courts through separate incidents. In December 2024, Sara Netanyahu filed a defamation lawsuit against Israel’s Channel 12 News following a report based on statements by Telegram channel host Udi Mizrahi. The broadcast alleged that sensitive security details, including information regarding an impending military operation against a Hezbollah leader, had been shared in private social circles. While the lawsuit highlighted anxieties over information management, the incident involved allegations of unauthorized verbal disclosures rather than a direct technical intrusion into a mobile device.
A far more concrete digital security failure emerged within the Prime Minister's immediate political staff, centered on senior aide Yonatan Urich. Urich, who resumed his advisory role in May after clearance from the Shin Bet security agency, developed a customized media monitoring system powered by Anthropic's Claude artificial intelligence model. The tool was designed to track real-time news coverage concerning Benjamin Netanyahu, his wife, and the ruling Likud party, automatically transmitting alerts and daily summaries to two private WhatsApp groups.
An investigation published by the Israeli newspaper Haaretz revealed that Urich inadvertently exposed the system's underlying source code in a public GitHub repository. The public availability of the code exposed operational details regarding how the custom monitoring application functioned, along with an underlying security vulnerability. Cybersecurity analysts noted that public repositories containing system logic can allow unauthorized third parties to understand automated workflows or gain unauthorized visibility into downstream notification channels. Haaretz reported that the exposed code and vulnerability were removed after reporters contacted Urich for comment.
Shortly after the technical flaws in the monitoring tool were identified, Urich experienced a direct breach of his personal communications. Excerpts from his private WhatsApp conversations began appearing online, featuring sensitive discussions with Likud politicians, pollsters, and prominent media figures. Haaretz examined the leaked material and verified its authenticity. In response, Urich issued a statement through his legal representatives on the social platform X, explicitly confirming that his personal messaging account had been compromised and threatening legal action against any outlets publishing the contents of the leaked chats.
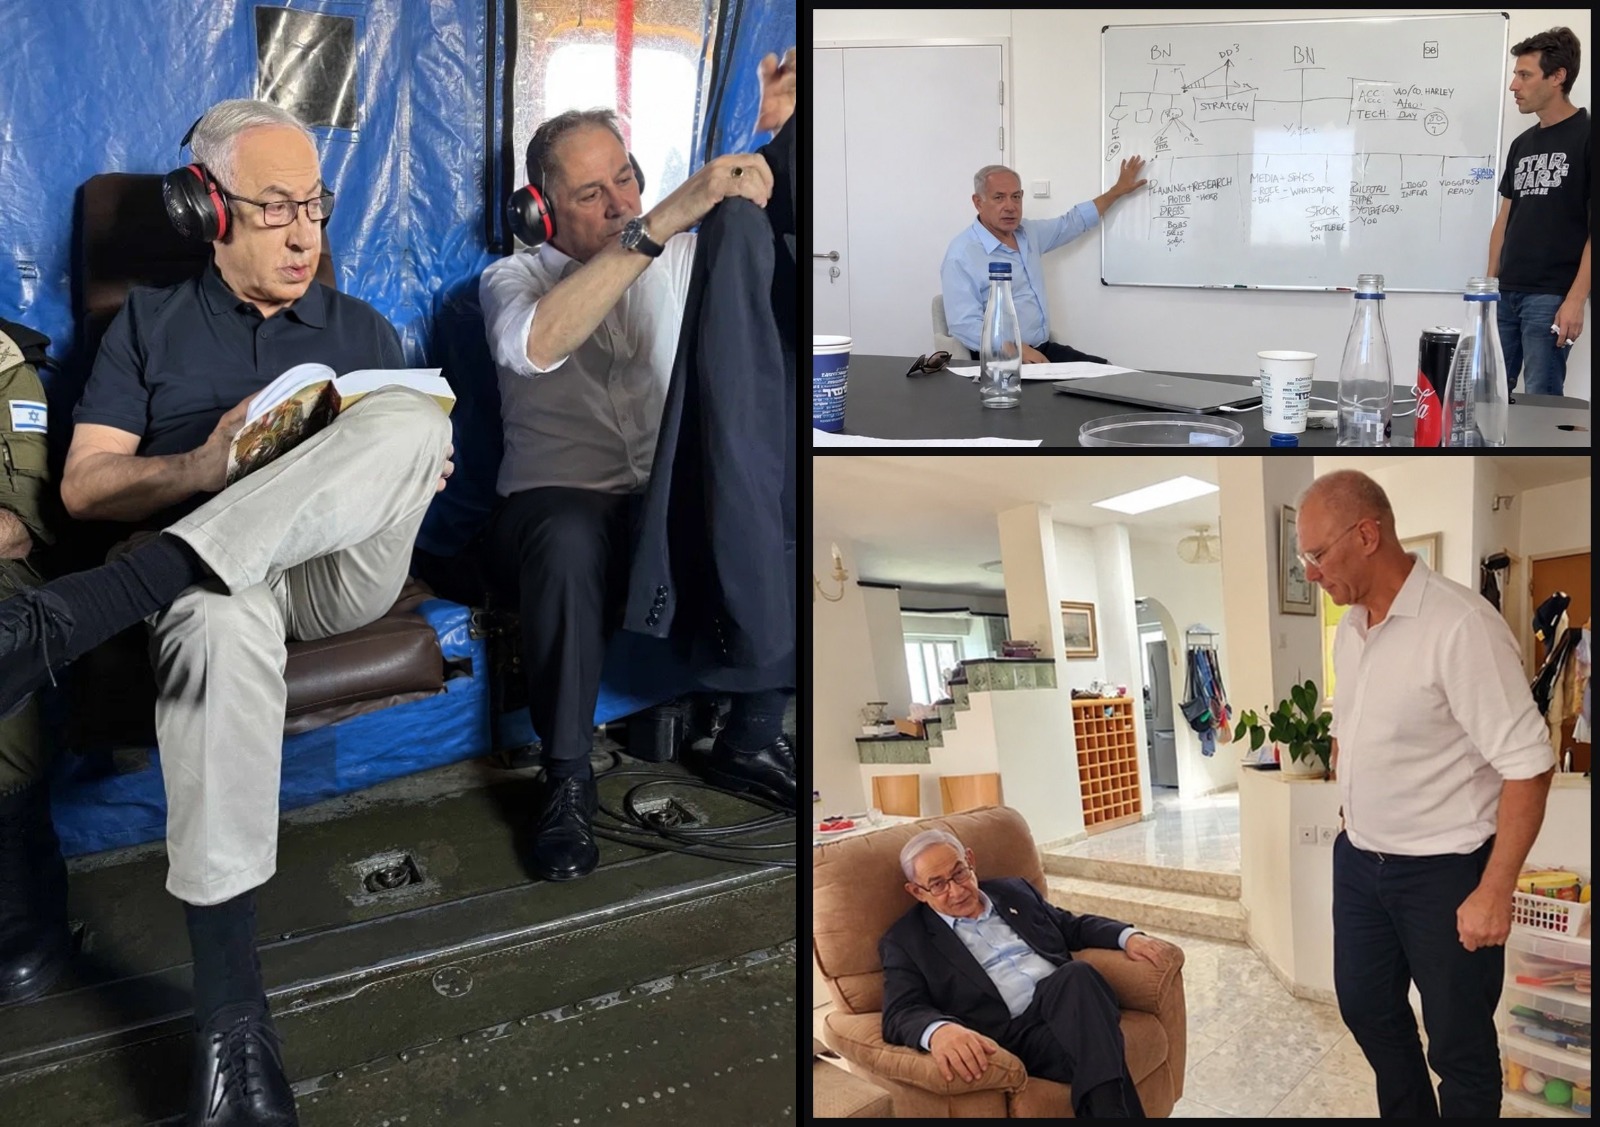
The timeline of the official security response to Urich's breach raised immediate questions among political and security observers. In October 2026, Haaretz reported that while the Shin Bet security service was actively investigating a separate breach involving Ambassador Yossi Shelley—after sensitive video footage taken aboard a military helicopter transporting the Prime Minister appeared online—authorities had not launched a formal investigation into Urich’s compromised account, despite the potential risk of foreign state access to high-level political communications.
The contrast between Israel's high-tech intelligence capabilities and the recurring security lapses around political leaders underscores a fundamental vulnerability: human operational security. Cyber defense experts emphasize that advanced encryption and elite defense networks cannot prevent failures caused by basic administrative mistakes. Exposed code repositories, weak access controls, unencrypted personal messaging, and susceptibility to social engineering remain standard entry points for intelligence gathering.
Threat analysts also note that claims of cyber intrusions are frequently weaponized as psychological operations designed to create political embarrassment regardless of whether a device was breached. Groups such as Handala have routinely claimed responsibility for hacking high-profile Israeli targets, blending real operational intrusions with exaggerated statements to amplify public anxiety. Sorting confirmed technical compromises from strategic disinformation remains a persistent challenge for intelligence agencies and news organizations alike.
For a nation renowned across the globe for penetrating some of the world's most secure digital networks, the recurring vulnerabilities surrounding Netanyahu's inner circle demonstrate that the greatest threat to sensitive communications may not be superior adversary technology. Instead, the persistent challenge lies in managing basic human operational security.